Businesses usually start working with AI solutions quite easily. A prompt is generated, the chatbot returns a valuable response, and the company sees the benefit: answering a customer’s query, summarizing the conditions of an agreement, describing a product.
Then comes the question, “Can we build this into our own software?”
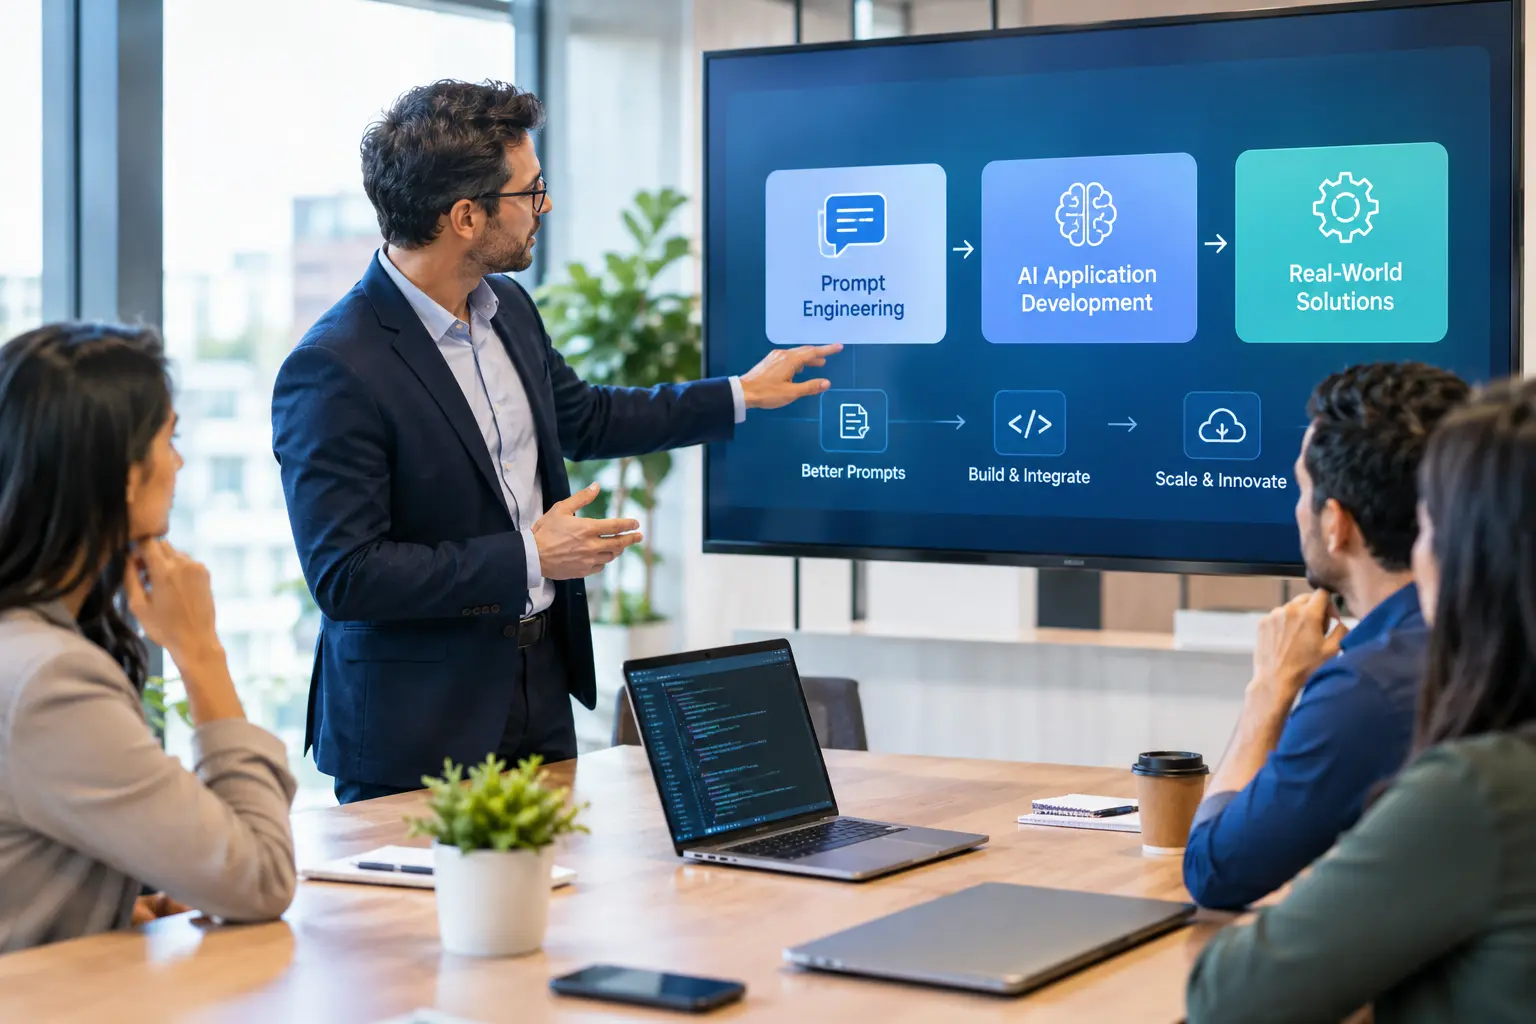
The process involved is far more complex than what can be seen in the demonstration. A prompt that may work well for one individual on one computer is quite different from an application that will be used by hundreds of customers or employees every day. Prompt engineering is the first step.
In this blog post, we will discuss the differences between prompt engineering and application development, when custom LLM development becomes a priority, and what should be done before hiring an AI app development company.
What Is Prompt Engineering?
The essence of prompt engineering is communicating with the models in their language. A large language model like GPT-4 and DALL·E will have different results depending on how you formulate the prompt.
Give a few examples and ask it to solve a problem step by step. “Write something about marketing” will give you some general text. “Write a 300-word LinkedIn post for CMOs with three actionable tips on applying AI in their campaigns” will give you something you can edit and publish.
It is also the most cost-effective method of testing the hypothesis. No servers are required; no development team is required; and in just one afternoon, you can find out what works well for the model and what does not work.
The problem with this approach is that the prompt serves only one user who then gets the output and corrects it. In a business application, there will be many users, unpredictable inputs, sensitive data, and normally no one would check all answers before the user gets them.
Things go wrong when a prompt turns into a product. These limitations generally manifest themselves during the first few weeks of using the model:
• Unreliable answers. The same question might receive different answers on different days. It is not harmful for slogans, but it is definitely problematic for a refund policy. Wrong answers that seem true. Sometimes models confidently give a false statement, and there is nothing in the answer that signals its unreliability to the reader.
• The lack of knowledge about your business. A generic model was never provided with your price list or internal policy.
• No access to your systems. The prompt can generate an email. However, it cannot check an order or update customer information unless it is connected to those systems by developers.
• No limitation on how it is used. Users will copy sensitive information into the prompt, ask irrelevant questions, or bypass any limitations you try to impose.
• No record of what happened. You will learn about problems only from your dissatisfied customers because there is no logging involved.
None of this is a reason not to employ the technology. These are simply the steps that have to be taken between the prompt and the dependable tool, and that is what AI app development is all about.
What AI application development covers
The language model is one component. Around it, a development team builds the parts that make it safe and useful for real users:
- Product definition. Who uses the product, what task does it perform, and how the success is going to be measured. This step is skipped too often, leading to automation of the wrong task.
- Data and retrieval. Retrieval-augmented generation (RAG) allows the model to find answers in your own documents, ensuring that the answers are based on your data and not just the general knowledge of the model.
- Orchestration. Prompt templates, model calls, tools and business rules have to be orchestrated. Versioning of prompts and separation from application code allow you to change one without breaking another, and swap model providers without a rewrite.
- Integration. Authentication, authorization, APIs, and connections to your CRM, database, and legacy systems.
- Safeguards. Validation of the input and output data and manual approval of risky operations such as refunds and deletion of records.
- Testing. Reliable way to test quality of the answers, covered in the next part of this article.
- Monitoring and costs control. Logging, performance, errors, monthly expenses, and alerts on quality degradation.
In most projects the model call is a small fraction of the code. The rest is ordinary software engineering, which is why an experienced AI app development company is judged mainly on its engineering practice and not on how clever its prompts are.
When custom LLM development is worth it
Custom LLM development covers a range of work, from light to heavy:
• Combination of prompting and RAG using a hosted model. Easiest solution, and frequently sufficient.
• Model fine-tuning. Additional training on top of a pre-existing model using your examples so that the model knows your lingo, style, or output format or can do a single thing well.
• Domain-specific or self-hosted models. Using an open-weight model within your own systems for security, compliance, or cost reasons.
• Training a model from scratch. Extremely expensive, and not usually justifiable for a business.
Most companies should not start at the heavy end. A well-built application on a strong hosted model, with good retrieval and proper testing, solves a large share of business problems.
Custom LLM development makes sense when:
- your field uses specialized language (legal, medical, engineering, finance) that general models handle poorly;
- your data cannot leave your own environment;
- you need consistent, structured output at high volume, where a smaller tuned model can be faster and cheaper;
- you have measured the gap, and testing shows the off-the-shelf approach falls short.
The last point matters most. Decide on customization from test results, not ambition. A good partner will tell you when you do not need it and show you the data behind that advice.
How to test software that gives different answers each time
Traditional software returns the same output for the same input, so a test can check for an exact result. Language models vary their wording, so exact matching does not work. “It looked right when I tried it” is not a release standard either.
The practical approach is to test behaviors instead of exact words:
• Define a good response. For customer service assistants, this could mean pointing out the true nature of the complaint, being polite and giving the correct follow-up.
• Gather some examples. Make sure you include the difficult ones – ambiguous queries, non-English input, weird formatting, angry clients.
• Run the system against the test set every time you make a change. It’s whenever you have a new prompt, dataset, or your AI vendor pushes an update to the model. Keep track of how well you’re doing, the pass rate, because “our pass rate is 85% and we are going up” is an actionable metric.
• Have another AI model check the output in terms of tone and involve people when it comes to subjective decisions.
This kind of testing allows you to enhance the product without destroying anything that works, and this is the main distinction between a prototype and a product. Providers also revise their models now and then, and the test set will reveal this change in behavior.
Security, privacy and compliance from day one
LLM applications suffer from the same software vulnerabilities, but some are unique to them. Prompt injection happens when a user crafts input text that makes the machine overlook its directives. Other types of security threats include data leaks and granting more permissions to the automated agent than necessary. The OWASP Top 10 for LLM Applications is a good starting point.
Before launch, get clear answers to these questions:
- What data is sent to the model, and where is it processed?
- Who can see the logs and conversation history?
- What can the system do on its own, and what needs a person to approve?
- Which regulations apply to your industry and your market?
You do not need every control on day one. You do need protection that fits the risk, planned from the start. Adding it in the last week before launch costs more and is usually incomplete.
Ownership and adoption
Two things end more projects than bugs do.
Nobody owns it. The person who developed the prototype may not be the best person to operate it. Every live service requires an owner of the business who is accountable for results, and individuals named for performance, incidents, user feedback, and supplier changes. This can be easy to set up, as long as the names are put in writing.
Nobody altered the process. If the tool does not suit the way that people work, they will revert to the old process. Determine what changes in roles and handoffs need to happen, when the users can trust the results, when they need to validate the results, and how they report an issue. Training your people on how to write good prompts is still valuable, since those closest to the action recognize bad answers first.
What to look for in an AI app development company
The partner you choose matters as much as the model. Look for these things:
• They begin with your challenge. Beware of those who suggest tweaking or developing an LLM without first understanding what you need to accomplish.
• They mention testing early on. If testing is mentioned only at the end, then quality will be there as well.
• They consider how they will work with your current systems. It is mostly about connecting to your data, processes, and previous tools.
• They have no problem talking about build, buy or integrate. Sometimes the best solution is a product that requires minimal customization.
• They are aware of post-launch considerations. Monitoring, model improvements, costs and other considerations should be included in the proposal.
- They leave you in control. You should own your prompts, your test data and your architecture documents.
A good AI app development company leaves your team better informed than it found it, not more dependent.
A practical route from prompt to production
You do not need to treat every experiment as a full product launch, because that would remove the speed that makes prototyping worthwhile. A short route with a clear decision point works well:
1. Define. Identify the user, the problem, the outcome you desire, the constraints, and the owner.
2. Prototype. Test the riskiest assumptions with the minimum viable product, using minimal data and minimal access.
3. Decide. Look at the data objectively, then decide to stop, iterate, buy, integrate, or build.
4. Harden and launch. Complete the engineering, testing, security, and support activities necessary based on the risk profile.
5. Improve. Observe real use, expand your test set and iteratively improve.
Final Thoughts
The deciding moment between step two and step three is critical. It ensures all involved understand whether they are testing an assumption or building a solution for use by the business.
PSSPL is an AI app development company that helps companies in transforming their prototype into a successful product, from selecting an appropriate use case to development of LLM. If you already have your prototype ready or just need some ideas to start with, feel free to contact us.